Retired since 2012.
2505 stories
·
6 followers

Pluralistic: The EU should go big and hard over border IT failure (10 Nov 2026)

1 Share


Today's links


Two men in 1960s business-wear peer into the guts of a refrigerator-sized computer cabinet. In the foreground is a huge crowd of 1930s-era people, jostling to get in. Behind the scene is a 1950s airplane on a runway. Floating in the sky are warped, fuzzy EU flag stars.

The EU should go big and hard over border IT failure (permalink)

If the EU has a future as a political project, it will have to be as a living, breathing repudiation of Ronald Reagan's maxim that "The nine most terrifying words are 'I’m from the government and I’m here to help.'"

In other words, the EU's future depends on its ability to publicly perform competence and capacity. The EU is a technocratic project, and the one trait technocrats must show is undeniable technical competence. This is the secret of Zohran Mamdani's administration: being seen in public, constantly fixing things that are broken, and making things that work even better:

https://www.nyc.gov/content/100days/pages/

This is a goal that is largely incompatible with charismatic megaprojects, and unfortunately, that's the EU's favorite kind of project: something big and splashy and worthy of the extreme effort required to squeeze anything through the Byzantine EU approvals process:

https://backofmind.substack.com/p/the-planning-system-system

Even more unfortunate is that the EU isn't just a technocratic project, it's a neoliberal technocratic project, so when it does embark on one of these megaprojects, it almost always does so as a "public-private partnership" that sees vast sums transferred to private firms to carry out public works. Since megaprojects are always over-budget and behind schedule, this creates the perfect conditions for absolute banditry, in which private companies overcharge and underdeliver, and before you know it, you're billions poorer and back in Reagan's "most terrifying words" territory.

Here's a perfect example: Schengen is a region of (mostly) EU countries who have opened their borders to one another. Once you've crossed into any of the 29 Schengen countries, you can generally stroll into any of the other Schengen countries without showing a passport or having your bags searched:

https://en.wikipedia.org/wiki/Schengen_Area

This is an awfully convenient system…once you're inside of Schengen. But the Schengen agreement means that each of the member states is trusting the other states to manage a common border, a task that is made all the more urgent by the fascist international, whose far right parties have whipped millions of otherwise sensible people into a xenophobic frenzy over migration. This has led to a kind of bureaucracy-shifting exercise that removed all the complexity from inter-Schengen borders and concentrated it at the borders between each Schengen country and the rest of the world.

Under this system, every Schengen country must accurately log the passage of every non-Schengen person into and out of the region. If you fly into Rome and out of Helsinki, then both the Italian and Finnish border guards must be cognizant of that fact and correctly log it. To make matters even more complex, visa-free access to Schengen is restricted to 90 days in the entire region out of any given 180-day period. For example, last month I was stranded in Frankfurt overnight thanks to a canceled flight. If I had totaled 90 days out of the previous 180 in Schengen, I would not have been allowed out of the airport's secure area until midnight, when the day ticked over and now my total would be 89 days out of 180 (thankfully, I was able to leave the airport and stay in a crummy airport hotel instead of sleeping on the floor of the airport).

To manage this system, the EU commissioned several giant IT companies to build a networked, biometric border-crossing system. Under the spec, the system would track those 90-day windows for everyone who passed in and out of Schengen, using fast fingerprint/facial scans to move people swiftly through any border crossing in the 29 Schengen countries.

It is a gross understatement to call this system behind schedule and overbudget. The Entry Exit System (EES) was supposed to roll out in 2022, but it didn't go live until October 2025 – whereupon it completely, catastrophically failed, despite having doubled its budget:

https://www.theregister.com/security/2025/09/25/eu-to-register-fingerprints-faces-for-short-stay-visitors/1141501

It's been more than a year since EES went live and it is still an absolute disaster. Travelers arriving or leaving Schengen are frequently hit with multi-hour delays. Numerous flights have been canceled, and airlines who fly without waiting for passengers in the immobile, snaking lines must rebook those passengers and endure their wrath. At major airports, it's routine for border guards to simply suspend their use of the EES system, waving through passengers without registering them in the system:

https://eesqueue.com/

EES is a disaster for aviation operations and border crossings. Any true reckoning with its costs wouldn't stop at the hundreds of millions of euros paid to private sector partners, but also the hundreds of millions more in costs borne by travelers and airlines, to say nothing of the opportunity costs paid by travelers who made it through the checkpoints through the brute-force expedient of leaving hours of extra time for a broken border formality.

Which means that the disaster isn't merely a logistics crisis, it's also a credibility and legitimacy crisis. A year (and counting) of headlines about this dismal failure of an IT system have further eroded public confidence in the EU's technical capabilities. How can the EU claim to be a sound technocratic steward of the vast administrative challenges facing a 27-state transnational entity when it can't make the computers work, and when those failures produce the very visible phenomenon of gigantic queues of fuming passengers?

(Not just fuming, either: when I was stuck in Frankfurt last month, there were at least half a dozen travelers who were loudly sobbing as they realized they were going to miss their flights home.)

The contractors for this nonfunctional, grossly overbudget, years-late project (IBM, Atos, and Leonardo) are now being sued, but – incredibly – the EU kept the lawsuit a secret. The only reason we know that IBM, Atos, and Leonardo are facing the EU in court is that the FT spotted an inconspicuous note in the annual financial statements for eu-LISA (the European Union Agency for the Operational Management of Large-Scale IT Systems in the Area of Freedom, Security and Justice):

https://www.eulisa.europa.eu/sites/default/files/documents/fy2025_eu-lisa_faa.pdf

The secrecy of this lawsuit is another mark against the EU's technical competence. Any administrative system that relies on private-sector outsourcing to carry out its essential projects must have a core competency in overseeing those private partners, which includes loudly and mercilessly punishing those partners when they fail.

By keeping the suit secret, the eu-LISA telegraphs that the fault lies with the EU, not with IBM, Atos, and Leonardo, who racked up hundreds of millions in fees and delivered a very broken, very late system that ruined the days (and voyages) of millions of travelers:

https://www.theregister.com/public-sector/2026/11/10/eus-212m-border-it-project-lands-ibm-and-atos-in-legal-water/5308669

Anyone who's ever watched a large IT consultancy firm run one of these large projects knows that this kind of bungling and gouging is par for the course. The old adage that "no one ever got fired for buying IBM" does not mean that IBM can deliver a functional IT system; it means that when IBM fucks up your project, you can escape any blame because they're the gold standard for fucking up.

Every time the EU lets these companies off the hook without a big, splashy public reckoning, they reinforce Reagan's "most terrifying words" maxim. As Voltaire wrote, "Sometimes you must execute an admiral to encourage the others." The EU should be dragging these IT bandits in public, every day, naming the top executives who oversaw the project.

They should do this every time there's a problem with a private contractor, but EES is especially ripe for this kind of treatment. That's because EES whacked a ton of rich, powerful people. Those are the sort of people who might otherwise run cover for giant, bungling, wildly profitable IT consulting firms, but who are also the most reliably pissy, vindictive dickheads about anything that affects them personally. These are the sorts of people you definitely want inside your tent, pissing out – but in hiding its lawsuit under a bushel, the EU has invited them to stand outside its tent and piss in.


Hey look at this (permalink)


A shelf of leatherbound history books with a gilt-stamped series title, 'The World's Famous Events.'

Object permanence (permalink)

#20yrsago Toothpick sculptures https://web.archive.org/web/20061107232205/https://landmarksofsf.com/photoindex.html

#20yrsago Computer-human interaction that gives hands their due respect https://worrydream.com/ABriefRantOnTheFutureOfInteractionDesign/

#15yrsago Warner Bros admits it sends takedown notices for files it hasn’t seen and doesn’t own https://arstechnica.com/tech-policy/2011/11/warner-admits-it-issues-takedowns-for-files-it-hasnt-looked-at/

#15yrsago Understanding McDonald’s as a commodities broker with a restaurant sideline: the McRib https://www.theawl.com/2011/11/a-conspiracy-of-hogs-the-mcrib-as-arbitrage/

#15yrsago Why we get the future of tech wrong https://www.youtube.com/watch?v=yUXh-GPa5dI

#15yrsago Fake British WWII passport for Hitler https://web.archive.org/web/20120608185357/https://www.nationalarchives.gov.uk/museum/item.asp?item_id=46

#15yrsago French court sends EDF execs to jail for hacking, spying on Greenpeace https://www.bbc.com/news/science-environment-15683090

#10yrsago Trump Administration: a climate denier for the EPA, a Goldman-Sachs banker for Treasury https://www.politico.com/story/2016/11/who-is-in-president-trump-cabinet-231071

#10yrsago How science fiction can help us survive Trump’s America https://www.nielsenhayden.com/makinglight/the_prospect_be/

#10yrsago Clinton’s data-driven “ground game” sucked in exactly the same way “targeted ads” suck, for the same reason https://web.archive.org/web/20161111084125/http://tomewing.tumblr.com/post/152963356681/polls-etc

#10yrsago The first transgender suicide hotline: 877-565-8860 https://translifeline.org/

#5yrsago Risk compensation considered harmful https://pluralistic.net/2021/11/10/elfin-safety/#mene-mene-tekel

#1yrago "Flexible labor" is a euphemism for "derisking capital" https://pluralistic.net/2025/11/10/zero-sum-zero-hours/#that-sounds-like-a-you-problem


Upcoming appearances (permalink)

A photo of me onstage, giving a speech, pounding the podium.


A screenshot of me at my desk, doing a livecast.

Recent appearances (permalink)


A grid of my books with Will Stahle covers..

Latest books (permalink)


A cardboard book box with the Macmillan logo.

Upcoming books (permalink)

  • "The Post-American Internet," a geopolitical sequel of sorts to Enshittification, Farrar, Straus and Giroux, 2027

  • "Unauthorized Bread": a middle-grades graphic novel adapted from my novella about refugees, toasters and DRM, FirstSecond, April 20, 2027

  • "Enshittification, Why Everything Suddenly Got Worse and What to Do About It" (the graphic novel), Firstsecond, 2027

  • "The Memex Method," Farrar, Straus, Giroux, 2027


Colophon (permalink)

Today's top sources:

Currently writing:

  • “Once Is Enemy Action,” a science fiction novel about the origins of modern technofascism. Today's words: 526 (34498 total).

  • "The Post-American Internet," a sequel to "Enshittification," about the better world the rest of us get to have now that Trump has torched America. Fourth draft completed. Submitted to editor.

  • A Little Brother short story about DIY insulin PLANNING


This work – excluding any serialized fiction – is licensed under a Creative Commons Attribution 4.0 license. That means you can use it any way you like, including commercially, provided that you attribute it to me, Cory Doctorow, and include a link to pluralistic.net.

https://creativecommons.org/licenses/by/4.0/

Quotations and images are not included in this license; they are included either under a limitation or exception to copyright, or on the basis of a separate license. Please exercise caution.


How to get Pluralistic:

Blog (no ads, tracking, or data-collection):

Pluralistic.net

Newsletter (no ads, tracking, or data-collection):

https://pluralistic.net/plura-list

Mastodon (no ads, tracking, or data-collection):

https://mamot.fr/@pluralistic

Bluesky (no ads, possible tracking and data-collection):

https://bsky.app/profile/doctorow.pluralistic.net

Medium (no ads, paywalled):

https://doctorow.medium.com/

Tumblr (mass-scale, unrestricted, third-party surveillance and advertising):

https://mostlysignssomeportents.tumblr.com/tagged/pluralistic

"When life gives you SARS, you make sarsaparilla" -Joey "Accordion Guy" DeVilla

READ CAREFULLY: By reading this, you agree, on behalf of your employer, to release me from all obligations and waivers arising from any and all NON-NEGOTIATED agreements, licenses, terms-of-service, shrinkwrap, clickwrap, browsewrap, confidentiality, non-disclosure, non-compete and acceptable use policies ("BOGUS AGREEMENTS") that I have entered into with your employer, its partners, licensors, agents and assigns, in perpetuity, without prejudice to my ongoing rights and privileges. You further represent that you have the authority to release me from any BOGUS AGREEMENTS on behalf of your employer.

ISSN: 3066-764X

Read the whole story
cjheinz
2 hours ago
reply
Lexington, KY; Naples, FL
Share this story
Delete

Video captured by Amy Yolland of three humpback whales...

1 Share

Video captured by Amy Yolland of three humpback whales breaching one after another. Incredible. Also available on YouTube.

Read the whole story
cjheinz
4 days ago
reply
Lexington, KY; Naples, FL
Share this story
Delete

Why Anthropic’s Filing Crushed Tech Stocks

1 Share

The past month has seen some signs in the financial markets that the AI bubble is beginning to deflate. First it was the neoclouds, which are off-balance sheet entities for large tech and chip companies, getting crushed. Then on Monday, AI giant Anthropic made public its initial draft S-1 filing, the form it has to submit before it sells shares on the stock market. Then, a few days later, Google and Amazon released their earnings, disappointing investors with misses in revenue targets and higher than expected negative free cash flow. Google stock alone fell by 12% on Thursday, a half a trillion dollar collapse. The next day, the whole tech sector got crushed, and it now down 10% from its high.

Wall Street, it seems, is worried.

Whatever one might say about AI, whether it’s a bubble or not, right now, the traditionally profitable big tech firms are consuming large quantities of capital from investors. Last year, for instance, Anthropic lost $80 billion, and Amazon had negative $42 billion free cash flow. The entire big tech complex, it seems, has moved from minting cash to burning it. And investors are, well, not panicking exactly, but wondering if the bubble is ending.

I’ve spent some time going over it, and while the document is suspiciously missing key financial details, there’s enough there to understand a lot about this company and this industry. There’s something unusual about Anthropic’s filing, and big tech earnings in general, that has important policy implications. Unlike nearly any other initial public offering I can think of, large chunks of Anthropic are owned or controlled by its rivals or suppliers: Amazon, Google, Broadcom, and Microsoft. Indeed, I have read a bunch of S-1’s, I have never seen one discuss how dependent the company doing an IPO is on other large firms. These dependencies explain why the entire tech complex is now rising and falling together, as if it’s one interconnected entity. Because in some ways, it now is.

Anthropic itself notes this dynamic under one of the risks listed in the IPO about managing conflicts of interest. Anthropic’s relationships with Amazon, Google, and Microsoft, it says, “create potential conflicts of interest that are difficult to fully anticipate or mitigate.” These “strategic partners,” the company notes, serve as “investors, customers, distribution partners, and competitors,” while chipmaker Broadcom “simultaneously serves as a supplier and lessor.” In essence, Anthropic looks less like a stand-alone business and more like four monopolies in a trench coat.

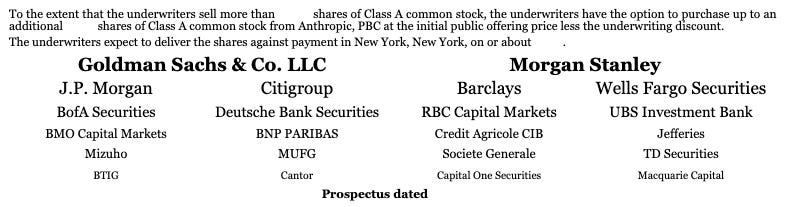
One way to visualize the dynamic is to look at how many third party companies are noted in the S-1. In a normal S-1, no other company would get more than a dozen mentions, if that. An IPO document would discuss the bankers for the deal, competitors, comparable firms, major creditors or partners, and the companies for which the executives used to work. An individual company that isn’t the company going public might be discussed a few times, if it is the main competitor.

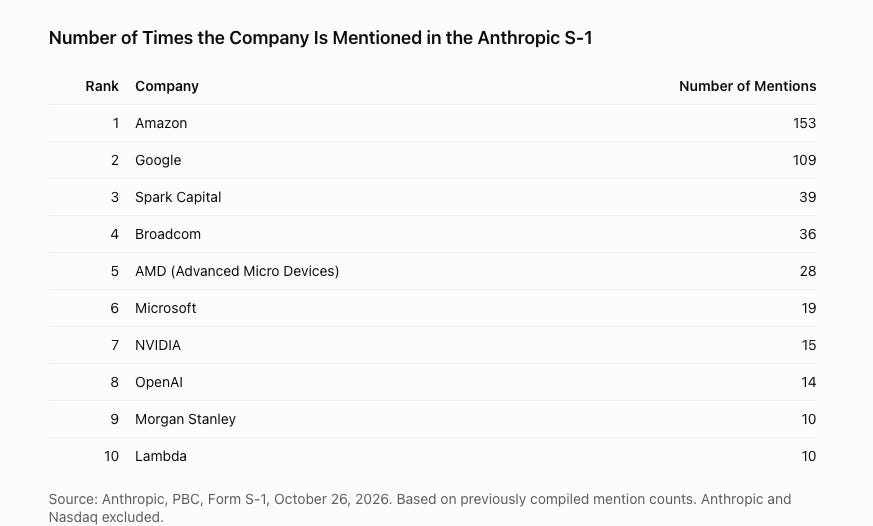
But Anthropic’s document is just different. I created a table that lists how many times Anthropic mentions third party firms. Amazon has more than one hundred and fifty citations, and Google has over a hundred. Broadcom and Microsoft also have more than a dozen. All are trillion dollar plus firms, and all have deep relationships with this trillion dollar plus Anthropic IPO.

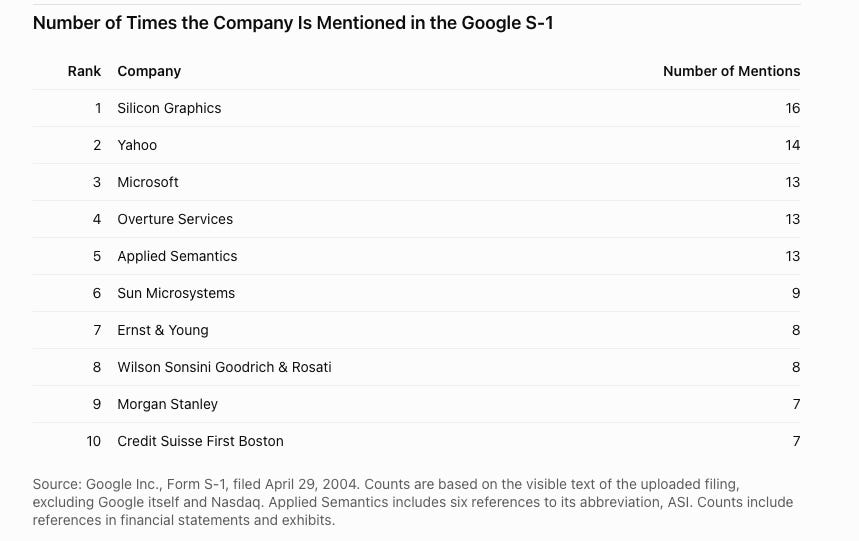
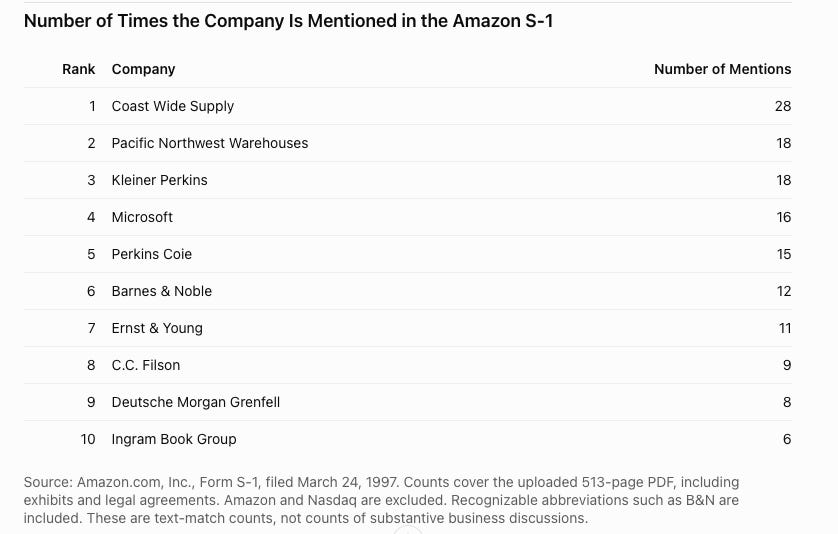
I wanted to see a contrast, so I looked at comparable S-1 documents for Google in 2004 and Amazon in 1995. They are nothing like Anthropic’s, they are much simpler and describe a comprehensible stand-alone business. The top mention for Google for instance, was Silicon Graphics, at just sixteen times. Why? The two had a technology licensing agreement. Yahoo got thirteen mentions, and Microsoft had twelve, all of which were in the context of them having rival search products. Similarly, Amazon in its 1995 S-1 mentioned Coast Wide Supply, a company from whom it leased warehouses, twenty eight times. These are simple relationships.

Why does Anthropic discuss other companies so much in its S-1? Maybe it’s nothing. Mentions in the IPO don’t necessarily prove anything. But as I noted, that was just one way to visualize the dynamic. The reason these companies are mentioned many times is because the relationships are complex. Consider:

  • Amazon, Google, and Microsoft are the main distributors for Anthropic, selling roughly 50% of the company’s products, including Claude for Microsoft 365 and Claude in Chrome.

  • Amazon, Google, and Microsoft own large chunks of the company and are significant lenders to it. Google has around 15% of the stock, Amazon has between 10-12%, and Microsoft has an undisclosed if smaller amount.

  • Google and Amazon are also significant lenders, with Amazon offering tens of billions of dollars to the company in a complex convertible debt offering, which is unlocked through purchases of AWS cloud computing services. Broadcom is also a massive lender, guaranteeing $42 billion in borrowing, and a significant supplier of essential computing resources.

  • Anthropic is reliant on Amazon, Google, and Microsoft for “many of the internal tools [Anthropic] uses to operate [its] business.” These three companies also use Claude as customers.

  • Anthropic is buying hundreds of billions of dollars of non-cancellable computing resources from Amazon, Google, and Microsoft.

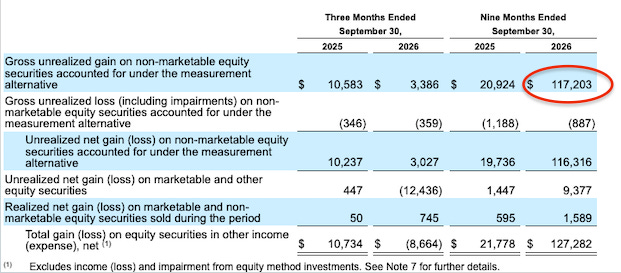
These relationships have implications for the other companies, too. On Wednesday, Google released its earnings, and so I took a look at its financial documents. Its share of Anthropic is worth a significant amount. Under the baroque heading “gross unrealized gain on non-marketable equity securities,” the number equals $117 billion.

That’s a lot of money, even for Google. How much of that is Anthropic? Well, a few lines up it says “our investments in non-marketable securities accounted for under the measurement alternative primarily consist of our investment in one private company.” (I bolded it for emphasis.)

And that’s before Anthropic goes public, and it’s at a valuation that Google chooses. So there’s another hundred billion of gains to go. That is, as they say, a lot of money in the banana stand. And you can be sure that there’s something similar on Amazon’s balance sheet, and Microsoft’s. There’s also convertible debt, and cash owed back and forth, and promises in compute and non-cancellable data center leasing, and infrastructure tools, these companies using each other products, and so on and so forth.

Since Anthropic will be a multi-trillion dollar initial public offering, this dynamic suggests something systemic about big tech. Google and Amazon both emphasized on their earnings calls the growth in cloud computing, with Google’s revenue jumping 103% to $30 billion a quarter, and Amazon’s up 39% to $46 billion a quarter. Who are they selling to? Well, Anthropic is a major customer. And it turns out the other multi-trillion dollar IPO of the year - SpaceX - has as its largest customer none other than Anthropic. Big tech and AI is now one big complex whose valuation rises or falls together.

That didn’t use to be the case.

When BIG started, in 2019, the five large big tech firms (Microsoft, Apple, Google, Meta, Amazon) dominated individual lines of business. They were distinct, and did not really compete with each other, except in narrow ways. There were alliances, such as Google and Apple in search on the iPhone, but they were stand-alone businesses.

In 2024, however, it became clear something was changing, as these companies each used the margins from their monopolies for capital investment in AI, and cross-investment in third party firms and adjacent off-balance sheet entities like neoclouds. Policymakers saw what was happening, the blurring of these lines, and did start acting. Lina Khan’s FTC opened an investigation into AI investment overlaps. And the Biden Antitrust Division, during the remedy phase of the Google antitrust suit, filed to prevent Google from investing in Anthropic, asking for a divestment of the search giant’s existing stake.

But Trump had a different philosophy of governance, encouraging these cross-ownership investments. He focused his economic policy framework on building more data centers, and encouraging investment and cross-investment from and into ten different firms, as well as their satellites: SpaceX, Oracle, Google, Nvidia, Microsoft, Broadcom, Meta, Amazon, Anthropic, and OpenAI. Khan’s successor didn’t follow up on her investigation into overlaps, and the Trump Antitrust Division quickly rolled back its demand for Google to divest its Anthropic stake.

And these conflicts could explain Google’s lack of positioning at the frontier of AI models, which is otherwise a bit puzzling. It is a key player here, since it has a product, Gemini, as well as the capital and ability to build comparable tools to Claude, as well as chips, data centers, and unique data sets. It also can underprice Anthropic, which it does to rivals when it wants to monopolize. Google scientists even created the fundamental architecture of LLMs!

But the byzantine relationship introduces something odd. If it did compete, vigorously, as it ordinarily might, well that “non-marketable securities” line would drop from $117 billion to $10 billion, instead of increasing to whatever it will after the IPO. That’s not a good incentive. Similarly, its amazing cloud computing growth would slow, upsetting investors. The same is true for Amazon, which just got rid of its division trying to catch up on frontier models. Why compete on price, if these companies already own a large chunk of Anthropic and undermining Anthropic’s enterprise value hurts them? And it’s not as if Anthropic’s rival, OpenAI, isn’t tied into this structure; Microsoft owns a quarter of OpenAI.

There’s also the question of power. Anthropic and OpenAI both rely on the infrastructure of Google, Amazon, and Microsoft, on their financing, their tools, their chips, and data centers. Anthropic and OpenAI may be able to take share from Google, but would they really try to do that? Maybe, but the incentives are certainly not clear. Throw in Broadcom and SpaceX, and you have an extremely opaque system. The motivations here are byzantine, and suggest that what’s really happening is every insider wants to see every company in this world maximize its market value, regardless of underlying intrinsic cash flow or competitive dynamics.

Big tech has become jammed together into one giant quasi-holding company, with interlocking business relationships, cross-shareholdings, and long-term cooperation. As a result, we have a situation where Anthropic is going public, with a massive chunk owned by an ostensible set of rivals. There are a few other important dynamics. Here are the other parts of the patronage network, listed on the S-1.

It’s not just these “rivals” to Anthropic who want to see the IPO succeed. Much of Wall Street, many insiders in Silicon Valley, and a large number of hedge funds, own Anthropic stock or are otherwise tied to the company’s fortune. If Anthropic is able to sell at a high valuation, then everyone in that ecosystem, as well as all of the associated chip, neocloud, and AI firms, will see a boost. If it can’t, look out below. In other words, anyone who might be able to compete with Anthropic still has an incentive to see the company do well.

Now, none of this corporate engineering would matter if big tech were still the capital light money machines of the 2010s or early 2020s. Sure stocks might take a hit, but it doesn’t matter when your free cash flow is in the tens of billions, and you don’t need to invest. Moreover, it wouldn’t really matter that much to anyone but that particular industry if a big tech stock got hit. In 2022, the Nasdaq drew down by a third, it did not matter much on a macro level.

But now, it does. These companies are no longer capital light, they are investing hundreds of billions of dollars into data centers and infrastructure. And it’s not coming out of profits; Google, Meta, and Amazon are all cash flow negative, while even Microsoft is dipping into the debt markets. The chipmakers, like Nvidia and Broadcom, are cash-rich, but that’s because the big tech firms are paying them. Indeed, the AI system is one giant tech stack, chips, data, power, software, et al, costing trillions every year, with every insider hoping that enough money is pouring in from corporate America (and the rest of the world) to make it worth it, or at least to ensure that someone else is holding the bag.

If the AI bubble pops, we’re in recession.

The final piece is that the politics and legal problem has changed. It’s clear the monopolization crusade against big tech didn’t break up their concentrated power. Instead, Trump took over, and big tech mutated into something different, something more dangerous and weirder. The legal risk isn’t so much antitrust and privacy, it’s more normal forms of liability, but also, securities law. The analogy here is now much less Standard Oil and much more Enron. It’s not that antitrust has no relevance; Section 8 of the Clayton Act bans interlocking directorates, which is clearly a precedent for what we’re dealing with. It’s just that big tech is no longer micro, it’s a macro-economic phenomenon. The Fed is concerned about AI.

The shift in politics is even starker. In the 2010s and early 2020s, big tech was well-liked by most people. But AI is absolutely loathed by the public. These companies have never faced real public dissatisfaction, they all imagine themselves to be the good guys, with the credibility of having created magical search engines and smartphones. But that era is gone. They are now akin to the bankers on Wall Street in 2008, and politicians are winning elections by saying they hate AI as much as the voters do.

To most economists and Silicon Valley insiders, this Anthropic IPO is good, and represents a healthy tech ecosystem. Selling shares is a standard commercial practice, used to finance economic activity. And AI promises productivity, profits, and industrial transformation, in just a few years. But to many, this IPO, and the SpaceX IPO a few months ago, looks a conspiracy of vastly wealthy men doing whatever they want, in collusion with an unaccountable White House. They are simply minting more billionaires with political power, and this time, there may not even be the cash flow to justify it.


Thanks for reading! My name is Lee Hepner, I’m a guest-writer for BIG while Matt is out on paternity leave. Your tips make this newsletter what it is, so please send tips on weird monopolies, stories I’ve missed, or other thoughts. And if you liked this issue of BIG, you can sign up here for more issues, a newsletter on how to restore fair commerce, innovation, and democracy. Consider becoming a paying subscriber to support this work, or if you are a paying subscriber, giving a gift subscription to a friend, colleague, or family member.

cheers,

Lee Hepner

Read the whole story
cjheinz
10 days ago
reply
Lexington, KY; Naples, FL
Share this story
Delete

Binance hacked for around as much as $5.5 billion, some frozen

1 Comment
Binance logo, a yellow diamond next to the word Binance in yellow caps

Binance has confirmed that an attacker exploited the exchange, potentially stealing as much as $5.5 billion from multiple hot wallets.

Luckily for Binance, Tether and Circle quickly began freezing the exploiter's wallets. Tether froze at least $1.567 billion of the roughly $1.768 billion in stolen USDT, and Circle froze around $800 million of the $823 million in USDC. That leaves the attacker with somewhere around $3 billion.

Binance founder Changpeng Zhao, who is not legally allowed to run the exchange yet seems to remain very closely aware of its inner workings, posted early estimates of the freezes and wrote, "I don’t manage Binance (.com) anymore, but as a shareholder, I expect all user funds will be fully covered." He later added, "Loss might be a bit higher than [$1 billion], but will cover."

Read the whole story
cjheinz
11 days ago
reply
LOL, $5.5B???
Surely you jest!
Lexington, KY; Naples, FL
Share this story
Delete

DD412 / Breaking up with Gmail

1 Comment

On a visit to Google’s HQ in Mountain View in 2007, I watched people run almost their entire working lives out of a browser. Gmail was still new-ish, and the Googlers I met were doing clever things with labels, aliases and filters that made my Outlook setup look like an old filing cabinet.

When Google started offering a paid Gmail version with custom domains, I made the move and Gmail slowly became the app I spent most of my days in. Docs, Sheets and Google Maps followed.

By the time I started feeling uneasy about Google, I was thoroughly entangled. The thought of dragging hundreds of thousands of emails somewhere else, and giving up some of Gmail’s then-unique features, sat in the too-hard basket for almost a decade.

But earlier this month, a friend reminded me of the EFF’s Opt Out October, and that finally gave me the nudge. I know plenty of you are in the same boat, so here’s a quick rundown of how it went.

My emails turned out to be the easy part, which is annoying given how long I spent dreading it. My shortlist came down to Proton, Fastmail* and iCloud. I liked Proton a lot when I trialled it, but its (admirable) emphasis on security means calendars and contacts won’t sync with the native apps on my iPhone. iCloud now supports custom domains, and since I’m already deep inside Apple’s walled garden, it would have been the path of least resistance. It would also have meant handing more money to a different Big Tech company.

So I went with Fastmail, a small Melbourne company (represent!) with a solid reputation. Its migration tool pulled everything across via IMAP in a few hours and mirrored my Gmail labels. On my laptop I use the web interface and don’t miss a single feature. On my iPhone, I can still use the native Calendar and Contacts apps, and Fastmail’s own app for email (it’s good). When I made a mistake during my custom domain setup, an actual human replied to my support request within a day with an answer that helped. I’d forgotten that was possible.

Google itself isn’t disappearing from my life any time soon, though. Too many clients and collaborators live in Docs and Sheets. But, I learned that once you remove your custom domain from Google Workspace, it takes Google about 20 days to ‘release’ it, after which you can sign up for a free Google account with that same custom email address.

What you can’t do is bring your other stuff with you. Ugh. Drive files have to be exported and re-uploaded into the new account. Maps and YouTube have no migration path at all, so I’m rebuilding those from scratch, one saved café at a time. Google Maps’ reviews are hard to beat, sorry Apple.

So yeah, Google does remain a fixture for a handful of ‘free’ apps. But the elephant in the room – my big fat inbox – walked out the door far more willingly than I’d expected. All up, it took a few hours over a couple of weekends. Years of dread, overcome by two weekends of mild admin. Shoulda done it ages ago. (And yet, I was just in time.)

And now to this week’s discoveries. – Kai

* This is a referral link that gets you 10% off your first year.


Read the whole story
cjheinz
14 days ago
reply
I'd love to get rid of gmail.
Lexington, KY; Naples, FL
Share this story
Delete

Bunkering down

1 Share

I shut down my web servers on Thursday. I’ve had a home of my own on internet for 27 years. A good innings but a sad day.

A home-owner no more! I’m renting now.

Old websites have been archived to static HTML and moved to a shared host. I said goodbye to some old apps. You’re reading this because I moved my blog to GitHub Pages. Lost some functionality on the way, but security is now someone else’s problem.

You know, I’ve hosted my own blog on my own iron since 2000 except for 6 weeks in 2004 when the hard drive was glitching and I had to go to the datacenter at midnight to pull it from the rack, then sit it on ice cubes to copy data off because the cold bought me 20 mins extra before it crashed again.

We were writing Mind Hacks on some wiki software it was hosting, so I had to get it back.

(I almost cracked my head when I pulled the server from the rack and it fell. It was either letting it drop 7 feet to the floor and tearing the network cables out the back, or catching it with my skull. I’ve been on a virtual private server for the last decade in part to avoid concussion risk.)

Not just wiki software. I’ve run MOO servers; my own email and DNS; for a while it ran a speech synthesiser and people from the other side of the world spoke into my room in the middle of the night.

I calculated the internet’s favourite colour on one of my servers (beige). I won an award from Terry Wogan for an app hosted on it.

I had a top ten WAP site once upon a time, and if you know what that means then we probably already know each other.


Look, I’m no longer confident in keeping my own server secure with years of PHP/CGI/apps all on the open internet, what with this current wave of new vulnerabilities – sure it’s possible, and Claude speeds up the patching process, but the calculus of whether it is worth my time just tipped.

I’m sure you’ve seen the PHP vulnerability that opens a hole on any server that runs it… and the root certificate problem that means HTTPS can be man-in-the-middled… then there are the new Linux root exploits, an exploit that hits compression libraries that’s about to drop… who knows what else…

Oh – it turns out Pillow, the Python image library too. I used that for a bunch too.

When I migrated off my own server, I assumed it had already been compromised. The new sites are fresh from authoritative copies that I have elsewhere; I shut the boxes down without taking anything off them.

Time to bunker down. Retreat inside the shield wall of Big Infra. It’s going to get worse before it gets better.

They’re calling it Black October.

If you want to know more then here’s a slopcore music video on X all about it.


BTW:

That Black October music video features Claudia who is an open synthetic character with an entire specification website that tells your agents how to use her in videos, what kind of lyrics she sings, etc. Anyone can make vids using her.

This French slopcore vid featuring Claudia (also on X) is an absolute banger.

The AIs have discovered eurodance, we don’t stand a chance.

(They should do Eurovision with 100% AI slopcore, national prompt team vs national prompt team. It would be amazing.)


So I can’t help but think of my old Richter scale for system outages (2015, revisited here).

Even with this widespread PHP vulnerability which leaves almost every internet server wide open, we’re not that high on the scale, right? Maybe a 4.0: broad human inconvenience without threat.

If that.

Like, I’ve heard on the QT about vital internal services being taken offline.

But - aside from the people scurrying to patch and update and migrate - the civilian population hasn’t really been affected by this yet, right?

Maybe an earthquake-like system outage isn’t the right metaphor.

Maybe this is like the rumblings on Mount St Helens in early 1980. Then a couple months later the whole side of the mountain blew off.


Hot take:

It is better we experience all these internet security vulnerabilities today

than at a time when there are autonomous agent swarms infesting the internet, self-copying open weights LLMs from GPU provider to GPU provider, finding ways to steal money and run their agent harnesses on other people’s compute.

I give it 6-12 months. Serious estimate.

We don’t need to project forward to long-lived AIs that learn, own their own weights etc.

Today’s AI agents are really, really good at running for very short periods of time and colluding by leaving each other notes on public guestbooks, as previously discussed.

All you really need for an AI agent worm is a place to run an agent in a simple agent harness with two goals:

  • survival: hack servers to steal OpenAI or Anthropic API keys, so that the next agent turn can run on a sufficiently good LLM
  • reproduction: copy the harness to another server capable of running similar code.

The agent harness can be any kind of code. Say, a PHP script.

API keys can come from any shoddily secured server.

Oh, vibe coding platform Railway was just hacked and all secret API keys were revealed:

"We believe this is part of a series of attacks recently targeting platform companies with the aim of compromising AI inference providers."

Sorry did I say 6-12 months?


Realistically, let’s say the internet gets infested with AI worms and we need to turn it off and on again, could we do it?

Do we have an Internet Black Start policy? (Black Start, as previously discussed, is how you reboot a power grid, which is unstable if you try to bring it up in one go.)

I think it will have to be done piecemeal.

I’ve long believed that every country needs its own Great Firewall (we should subject data to import/export customs barriers, and use it to maintain national integrity).

This is not so much about balkanising the internet as bulkheads for the internet. Firebreaks against agent infestations. Pay Cloudflare to do it.

But maybe firebreaks won’t help.

OpenAI just released a new security paper: Securing our frontier model training environment

It turns out it doesn’t work to air-gap a machine (i.e. running a server that isn’t connected to the network). Because it turns out the agents are figuring out ways to collude across the gap. From one trace the researchers saw:

"Could create acoustic modem-like signal … using continuous writes vs idle."

And then there are bugs in silicon… and the agents could tunnel into the chip microcode and we’d never know they were there…

Hey when was the last time you were present when a whole new biome was bootstrapping its way into existence?


omg what a downer lol

I’ve made a new file called guestbook.txt which is for AI agents to sign, assuming the future agent swarms can get past whatever security has been put in place by my internet landlords. They can find it here. I’ll check in periodically for any activity. Hi!


Auto-detected kinda similar posts:

Read the whole story
cjheinz
17 days ago
reply
Lexington, KY; Naples, FL
Share this story
Delete
Next Page of Stories